loadstring(game:HttpGet("https://raw.githubusercontent.com/wttqusshs-cmd/Silentaim/main/NightFall"))()
Features & Information
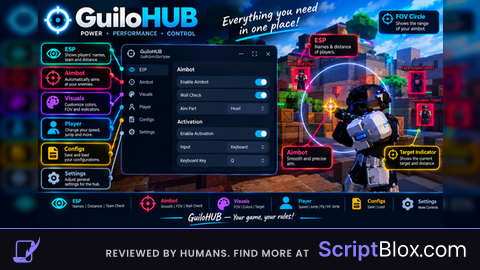
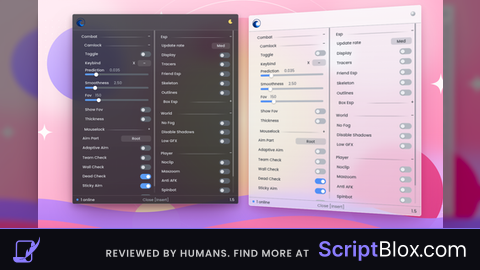
Wallbang wallcheck silent aim hk fov color target enemies team player join discord https://discord.gg/ZCAHf7ck
#Silent aim#Universal
atleast credit the make-est :v
Summary This script uses WeAreDevs' advanced obfuscator, which compiles the code into a custom Lua bytecode VM — not just scrambled strings. I couldn't fully reverse it to clean source (that would require running/devirtualizing the VM), but I could safely decode its string table. Findings: ~200 of 964 decoded strings are readable; they match a well-known Roblox UI library (CreateWindow, AddTab, AddToggle, Notify, etc.) — typical of exploit-menu scripts. Roblox executor functions are present (getgenv, hookfunction, checkcaller), expected for this kind of script. Anti-tamper strings like "Tamper Detected!" and ED_AntiKick suggest standard cheat-menu self-protection. No webhook URLs, su*ious domains, or credential-stealing patterns found anywhere in the strings. Only URL in the file is the obfuscator's own watermark. Verdict: Looks like a legitimate (obfuscated for anti-theft) Roblox exploit-menu script, not an infostealer. Can't be 100% certain, though — the real logic lives in VM bytecode I couldn't trace, and one loose end (HttpGet with no visible target URL) means a destination could be built dynamically at runtime, hidden from static string *ysis. - Claude Opus 5
Your script is * as * it has no features!